Don't hand your AI an API key: a safer way to let it act in your ERP
Giving an AI a credential is the fastest way to let it act — and the fastest way to lose control of what it does. Here is the difference a governed layer makes.
By DataTetherz
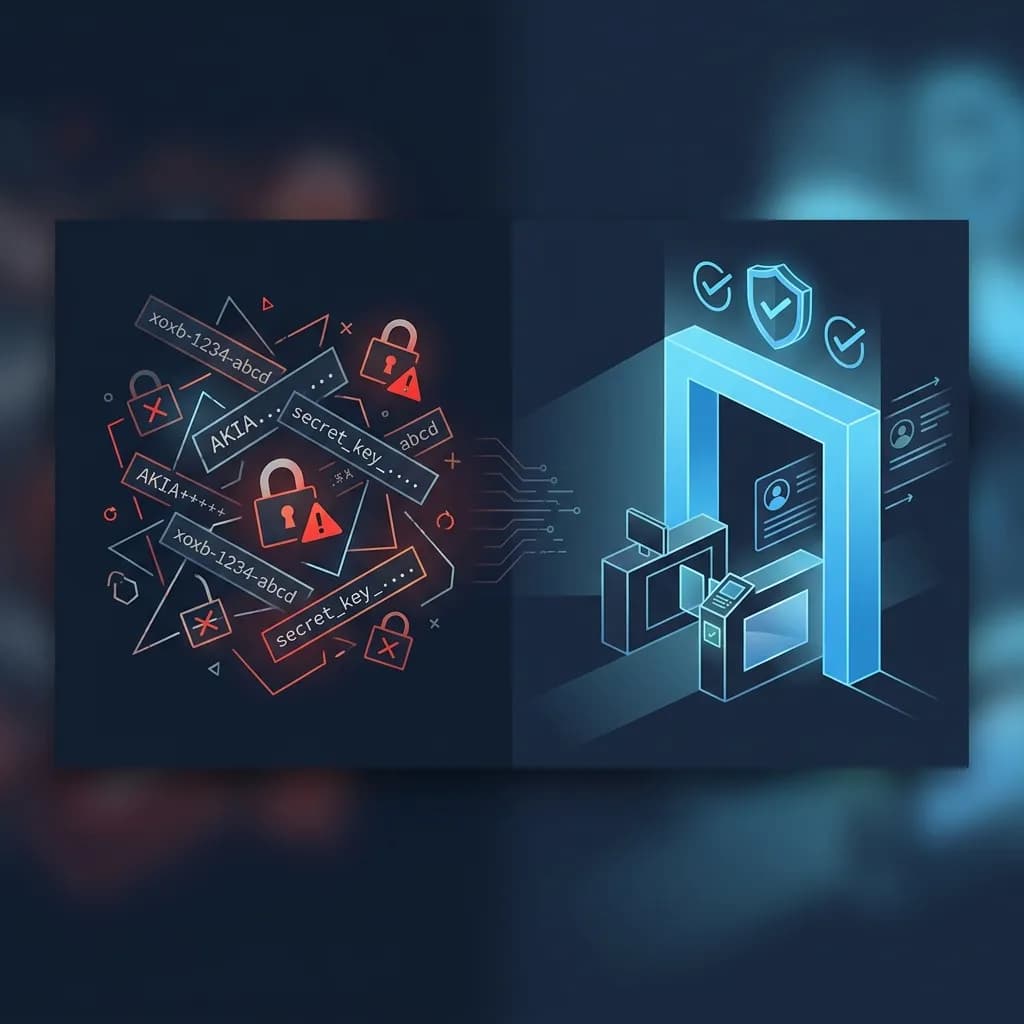
There is a tempting shortcut when you want an AI assistant to do real work in a system: just give it an API key. It works immediately. It also hands an autonomous caller broad, instant, unreviewable access to a system that runs your business.
For a side project, fine. For your ERP, that is a problem you will eventually have to explain to an auditor.
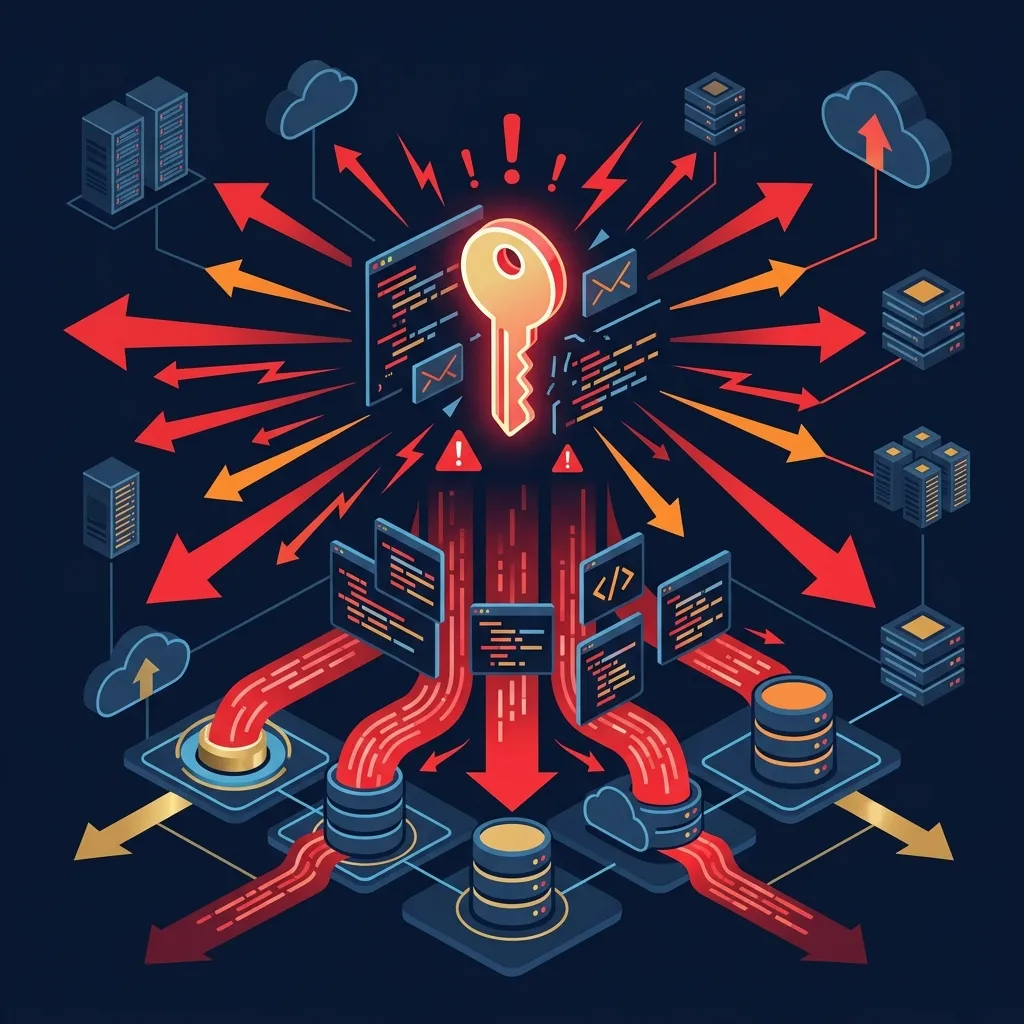 The risks of exposed API keys — credential leaking, over-broad access, and unreviewed writes
The trouble with keys-to-the-AI
An API key is a blunt instrument. Whoever holds it can do everything the key allows, the moment they ask, with no review and no record of intent. Give that key to a model and a few things become true at once:
- The credential is now copied into a client, cached, and easy to leak.
- The AI can reach far more than any single task needs.
- A write executes the instant the model decides to make it.
- When someone asks "who approved this change?", there is no answer.
None of these are exotic edge cases. They are the default behavior of the shortcut.
A supervised door instead of the keys
A governed MCP layer changes the shape of the problem. Instead of giving the AI the keys to the building, you give it a specific door — one that is checked, scoped, approved, and logged.
| What matters | Direct API key | Governed MCP layer |
|---|---|---|
| Credentials | Handed to the AI, easy to leak | Stay in a vault, resolved per request |
| Access scope | Whatever the key allows | Only what you exposed |
| Writes | Execute instantly, unreviewed | Held for a named human to approve |
| Audit | No clean answer | Identity, payload, approver, outcome logged |
| Revocation | Rotate the key everywhere | Turn off one tool or connection |
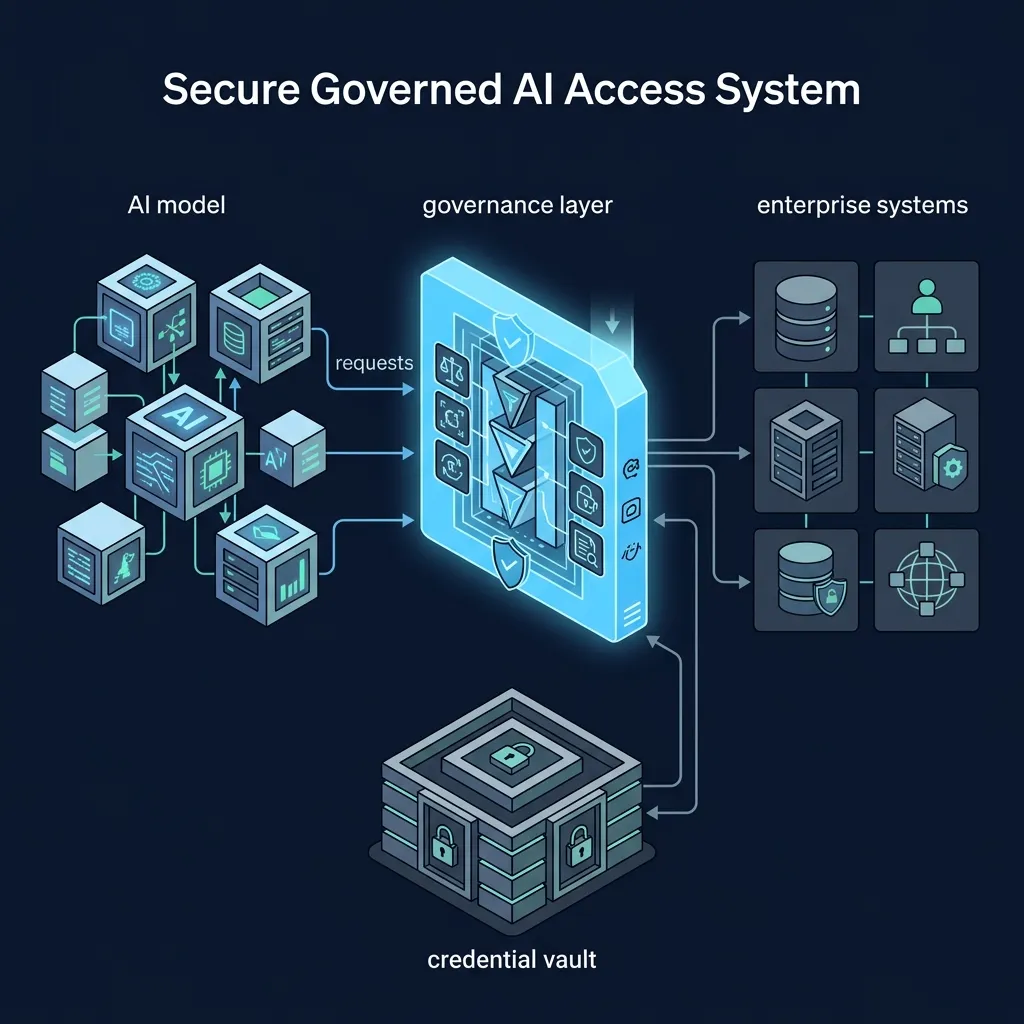 A governed MCP layer — AI requests flow through scoped access, approval gates, and audit logging before reaching enterprise systems
The difference isn't a feature checklist. It's that every hard security question already has an answer — and the answer comes with a log.
Why this is worth the small extra step
The productivity you want from AI acting in your systems is real. So is the risk of handing it a credential and hoping it behaves. A governed layer lets you keep the first without taking on the second: credentials never touch the model, scope is enforced in the middle, and the safe path is the default rather than something a developer has to remember to switch on.
Fast is good. Fast and defensible is the version that survives a security review.
See how DataTetherz enforces this governed layer by default in our security and governance documentation. When you're ready to move from prototype to production safely, the four-stage path shows how governance fits in from the start.